AS Path Length Calculator
Compare BGP route preference, AS path prepending, local preference, MED, peer relationship, route age, per-hop latency, competing routes, and manual policy weight.
Calculation breakdown
| Prepend count | Visible AS path effect | Typical use | Risk |
|---|---|---|---|
| 0 | No added ASNs | Primary, customer, or low-latency preferred path | May attract more inbound traffic than desired |
| 1 to 2 | Lightly longer path | Bias traffic away without hiding reachability | Some networks ignore small differences |
| 3 to 5 | Clearly less attractive route | Backup transit, secondary region, partial drain | Can over-shift traffic if peers honor path length strongly |
| 6 or more | Very long advertised path | Last-resort failover or emergency steering | May create unstable or surprising inbound choices |
| Order | Attribute | Winner | Operator note |
|---|---|---|---|
| 1 | Weight or policy | Highest local policy | Vendor-specific or route-map logic can override everything below. |
| 2 | Local preference | Highest value | Best knob for outbound routing inside your AS. |
| 3 | AS path length | Shortest path | Prepending influences inbound choice only when upstreams accept it. |
| 4 | MED and tie-breakers | Lowest then stable tie | MED, eBGP over iBGP, route age, and router ID come later. |
| Peer type | Score adjustment | Why it matters | Good default |
|---|---|---|---|
| Customer route | Strong preference | Customer routes often have revenue or administrative priority. | Prefer unless policy says otherwise |
| IX peer or CDN | Mild preference | Often short, cheap, and low-latency for eyeball or cache traffic. | Prefer for matching regions |
| Primary transit | Neutral to mild cost | Stable default path for full-table reachability. | Keep clean and lightly prepended |
| Backup or scrub path | Strong de-preference | Used for failover, DDoS mitigation, or expensive traffic handling. | Prepend or lower local preference |
| Scenario | Inputs to watch | Preferred outcome | Practical check |
|---|---|---|---|
| Primary transit | Local pref, route age, MED | Wins under normal operation | Confirm no accidental prepends on production prefixes. |
| Backup transit | Prepend count and policy weight | Loses until primary fails | Test reachability from external looking glasses. |
| IX peer short path | Peer type and latency hint | Wins for local traffic | Verify prefix filters and max-prefix limits before advertising. |
| DDoS scrub path | Policy weight and local pref | Wins during mitigation only | Automate route-map changes and rollback timing. |
This calculator is a planning model. Real BGP decisions depend on each network's route policy, communities, filters, route reflectors, and vendor-specific tie-breakers.
If you’ve looked at a network map you’re probably familiar with one that’s drawn like it was played in hopscotch around the world. While that visualization help, what it obscures is decision making occurring within each router along the way. Routes aren’t selected by BGP because they are visually appealing on a drawing. They are selected according to a strict and ordered set of attributes.
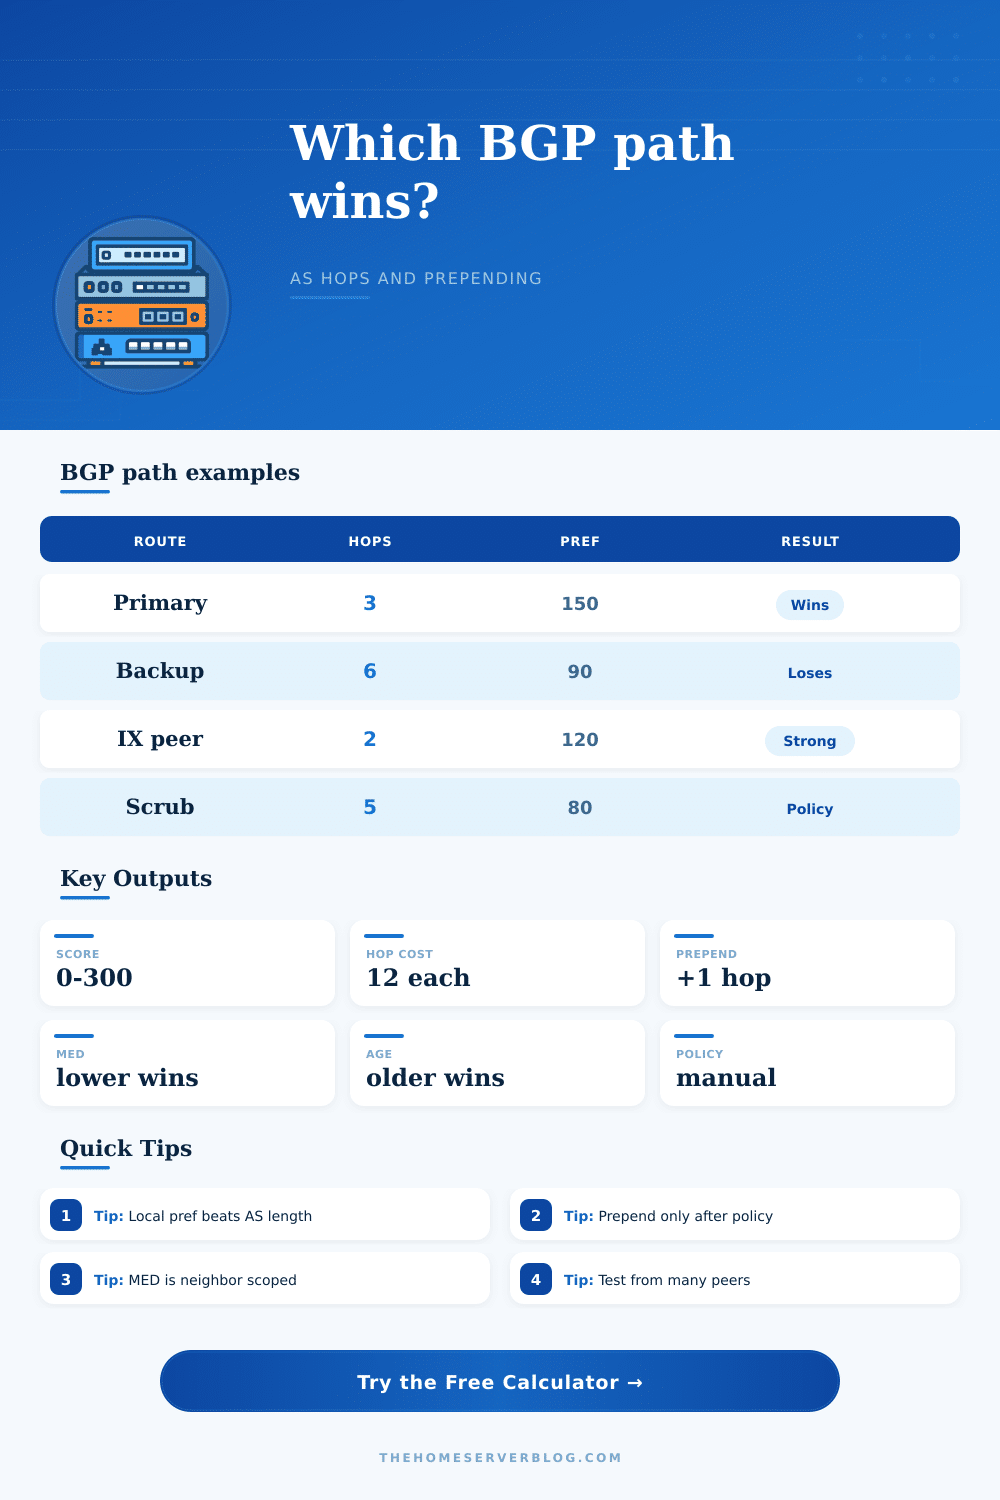
While the AS path length calculator will do math for us, true understanding is knowing how it values things it evaluates. For example, most folks consider local preference to be a simple volume control. Turn it up, traffic goes this direction. It misses the subtlety. Because local preference function prior to any consideration of path length or number of hops, it is a powerful tool in the protocol toolkit. It is base policy of your autonomous system.
How BGP Chooses Routes
Your primary transits have higher routes, so if you want to push outbound traffic there, done. That’s the shorter AS path via the backup link? Meh, you can lower local preference on it if you really want. That’s an order meant to keep topology separate from business logic. First, you say “this contract and this cost means I want my traffic here”. Second, then you have mechanics of how protocol routes traffic.
If there are ties locally, BGP consults the path length in AS space. That’s where prepending enters the picture. Prepending adds your ASN to the beginning of a route, causing it to appear longer to your peers. They see additional hops, so they think you don’t want them sending traffic down that path. It’s a polite way to steer inbound traffic without altering your own internal policies.
But like all things political, polite only goes so far. Different upstream providers treats prepends differently. Some will give more weight to three additional ASNs. Others won’t care if the difference is small at all. The calculator provides you with policy weights for each type of peer, showing those behaviors. Path lengths might be equal, but a customer route might be weighted higher than an IX peer. This happens because real-world operators prioritize strategic importance and traffic generation over short cable length.
Prepending is dangerous because of the potential to overcorrect. Too much prepending can cause your route to appear flakey or otherwise broken. If path is too long, routers may drop it. The table on page spells this out well. They give a variety of numbers of hops prepended and how those counts affect visibility. Generally speaking 3-5 additional hops will indicate they strongly prefer another path. Anything six or more and you risk being hidden entirely. There’s a fine line between getting someone to use you and being reachable at all.
Keep in mind, however, Multi Exit Discriminator values as well. When you have multiple links into a given neighbor, MED tells them which one you want them to take. Lower number wins, but only inside that neighbors view of things. Different neighbors aren’t going to compare your MEDs to see who gets it. This is where lots of engineers get hung up thinking MED should be global. It isn’t.
Another part of stability logic is age of the route. Steady-state is indicated by older routes and we tend to prefer them. The idea is: flapping routes gets suppressed so that there isn’t any churn around the Internet. When you fail over from one link to another, the new path has an age of zero. Unless your policy explicitly prefers it, router may stay on the older (slightly less optimal) path simply for stabilitys sake.
BGP doesn’t care about speed. BGP cares about what it sees, protocol attributes, nothing more. So you could have a short AS path, but it might go through some very congested nodes, causing high packet loss. But as long as the attributes line up, the protocol will prefer it anyway. And this is why it’s always important to test from external looking glasses. You can predict policy outcomes using a calculator, but you could of predicted how they perform in practice.
Ultimately, this is all about intent. Every characteristic is there for forcing a decision. Outbound traffic flows based on local preference. Inbound direction is based on AS path length. Multi-homed entries are further refined by MED. Knowing the order in which these attributes apply will help you avoid being frustrated with unexpected traffic flow. Instead of wondering why something got lost, you’ll begin to understand how it was judged along the policy stack.
Because math is deterministic. The hard part is making sure you feed it with right inputs to match your business goals. Make your primary paths very preferred and keep them clear. Add your backup paths sparingly. Validate your neighbor’s view of things by testing from various perspectives. From the outside looking in, path appears straight-forward. But inside is where math of global connectivity is calculated.
Learn that math and you won’t just react to an outage; you will design around it.